Security Engineer at Wazuh
Feb 2025 - Present
events through tuned pipelines
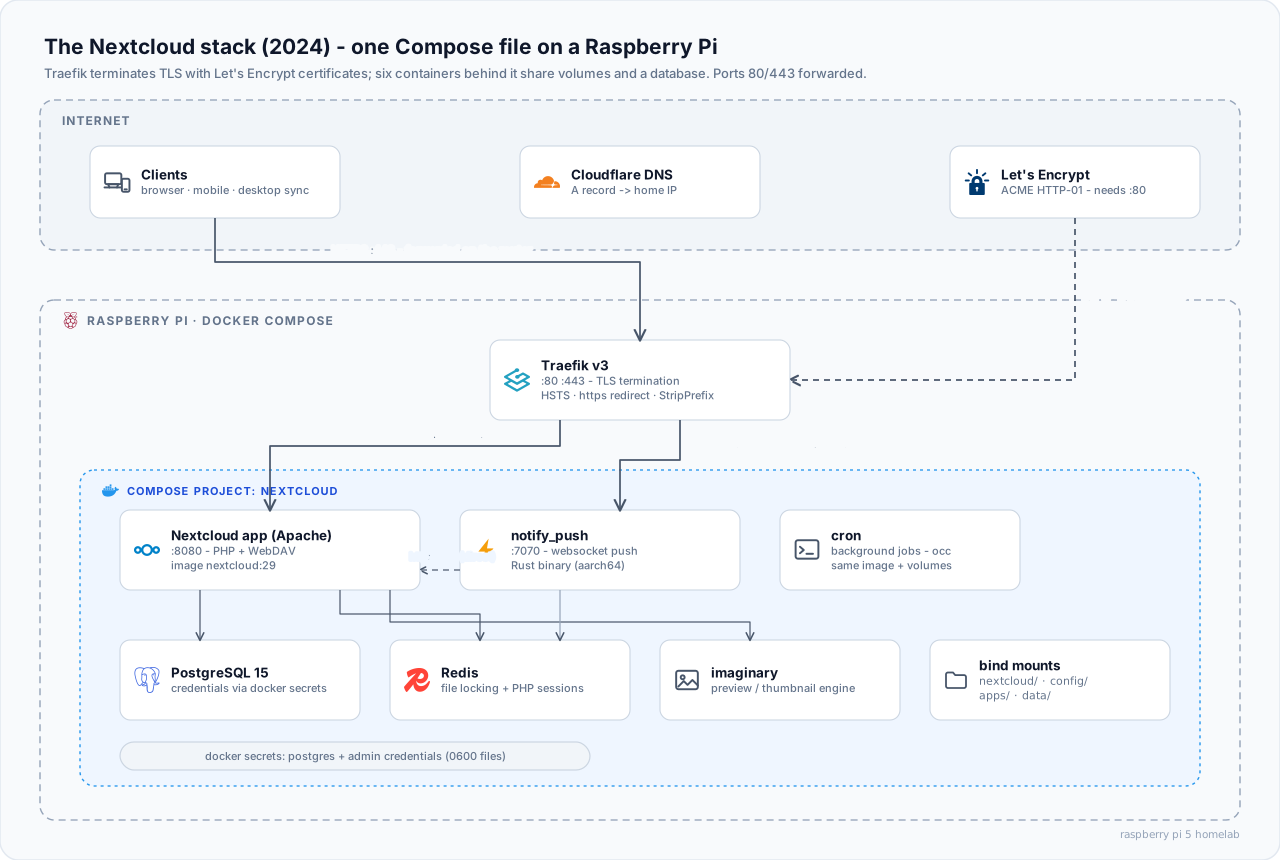
Tuned every stage between the agent and the index so bursts never drop events.
Tuned ingestion pipelines processing over 250B events by profiling backpressure across analysisd queue depths, decode and rule-matching worker threads, Filebeat batching, and OpenSearch index buffer throughput. Correlated queue buffer saturation against event-to-index latency and dynamically adjusted memory limits to absorb sudden burst traffic without dropping agent events or exhausting host resources.
cloud cost
Up to a fifth off the AWS EKS bill without losing indexing throughput.
- Right-sizing instance types to the real load
- ARM → AMD for indexing-heavy pods
- ISM tiering of old indices to warm and cold S3
Reduced AWS EKS infrastructure costs by up to 20% through instance right-sizing, migrating multi-pod workloads from ARM to AMD instances for optimized indexing throughput, and implementing OpenSearch Index State Management policies to transition aging indices to warm and cold S3 storage tiers.
platforms integrated
Rules, decoders and connectors shipped in the public Wazuh integrations repository.
 AWS
 Google Cloud
 Azure
 Active Directory
 Microsoft 365
 Google Workspace
 Okta
 FortiGate
 Sophos
 Cisco
compliance frameworks
SCA baselines and controls mapped per agent group.
- PCI-DSSPayment Card Industry Data Security Standard
- CJISCriminal Justice Information Services
- ISO 27001Information security management
- HIPAAUS health data privacy and security
- GDPREU General Data Protection Regulation
- NISTNIST Cybersecurity Framework
Cluster architecture
Multi-node Wazuh + OpenSearch clusters on AWS EKS, Google Cloud, Azure AKS and Proxmox — replicas across zones, instant agent failover.
 AWS EKS
- Google Cloud
- Azure AKS
 Proxmox
Architected multi-node Wazuh and OpenSearch clusters across on-premises and hybrid cloud environments, AWS EKS, Google Cloud, Azure AKS, and Proxmox, using EC2 or ECS when managers ran outside Kubernetes. Spread pod and index replicas across availability zones around an active master for cluster coordination, enrollment, and the API, scaling worker pools horizontally with pod anti-affinity to ensure immediate agent failover upon worker disruption.
Ingestion tuning
Tuned queues, worker threads and index buffers so traffic bursts never drop agent events.
Tuned ingestion pipelines processing over 250B events by profiling backpressure across analysisd queue depths, decode and rule-matching worker threads, Filebeat batching, and OpenSearch index buffer throughput. Correlated queue buffer saturation against event-to-index latency and dynamically adjusted memory limits to absorb sudden burst traffic without dropping agent events or exhausting host resources.
Cloud cost
Right-sized instances, moved indexing from ARM to AMD, and tiered old indices to warm/cold S3.
Reduced AWS EKS infrastructure costs by up to 20% through instance right-sizing, migrating multi-pod workloads from ARM to AMD instances for optimized indexing throughput, and implementing OpenSearch Index State Management policies to transition aging indices to warm and cold S3 storage tiers.
Incident recovery
Brought enterprise clusters back from disk pressure, split-brain and ingestion stalls.
Restored security visibility and cluster stability for enterprise customers during production outages caused by ingestion bottlenecks, disk pressure, persistent volume exhaustion, split-brain states, and indexer cluster degradation.
GitOps & observability
Declarative EKS deploys that roll back on SLO breach; Prometheus and Grafana on every queue.
Engineered declarative GitOps deployment workflows for EKS clusters versioned in GitHub with pod disruption budgets, rolling updates, and health-checked automated rollbacks when ingestion lag or worker queue saturation breached predefined SLI/SLO thresholds. Instrumented Prometheus, Grafana, and OpenSearch telemetry around cluster queues, memory pressure, and index write latency with automated runbook routing to resolve pipeline stalls before log loss occurred.
Integrations
Core maintainer of the public integrations repo: rules, decoders and connectors for 10 platforms.
- AWS
- Google Cloud
- Azure
- Active Directory
- Microsoft 365
- Google Workspace
- Okta
- FortiGate
- Sophos
- Cisco
Maintained the Wazuh public integrations repository as core maintainer, authoring and shipping detection rules, decoders, IOC lookups, alert enrichment, threat intelligence feeds, active-response scripts, SCA policies, and custom integrations for AWS (SQS, CloudTrail, VPC Flow Logs), Azure (Microsoft Graph), Microsoft 365, Okta, Entra ID, Active Directory, Google Workspace, LDAP, FortiGate, Sophos, and Cisco.
Response playbooks
Correlation, enrichment and active response with circuit breakers — automation without alert storms.
Built Wazuh response playbooks where correlation rules identify temporal patterns across shared attributes, IOC and enrichment scripts append threat context, and active-response commands execute against targeted endpoints with strict execution timeouts and circuit-breaker rate limits to prevent alert storms. Channeled alerts and automated ticketing through enterprise integrations while reserving host isolation and credential actions for analyst review, maintaining high detection fidelity through frequency thresholds, exception grouping, and benign-case baseline validation.
Compliance
SCA baselines mapped to PCI-DSS, CJIS, ISO 27001, HIPAA, GDPR and NIST; TLS syslog into air-gapped VPCs; least-privilege RBAC.
- PCI-DSSPayment Card Industry Data Security Standard
- CJISCriminal Justice Information Services
- ISO 27001Information security management
- HIPAAUS health data privacy and security
- GDPREU General Data Protection Regulation
- NISTNIST Cybersecurity Framework
Developed SCA baselines mapped to PCI-DSS, CJIS, ISO 27001, HIPAA, GDPR, and NIST, assigned by agent group, and ingested device telemetry with rsyslog over TLS into internal Network Load Balancers inside air-gapped VPCs with egress strictly restricted to proxy allowlists for OS updates and vulnerability feeds. Enforced least-privilege separation across Wazuh APIs and OpenSearch index patterns using role-based access controls and identity provider synchronization, deploying detection content only after staging validation, backup verification, and approved change windows.




 Machine Learning A-Z
 Master C++ Programming
 GameJam Pichola
 Video Game & Entrepreneurship Program